AI Agent Security for Claude
Check Claude agent actions before they reach your apps
See what Claude Code and Cowork agents can reach, cut the access they don’t need, and check each tool call against your policy before it runs.
Trusted By


See what Claude Code and Cowork agents can reach, cut the access they don’t need, and check each tool call against your policy before it runs.
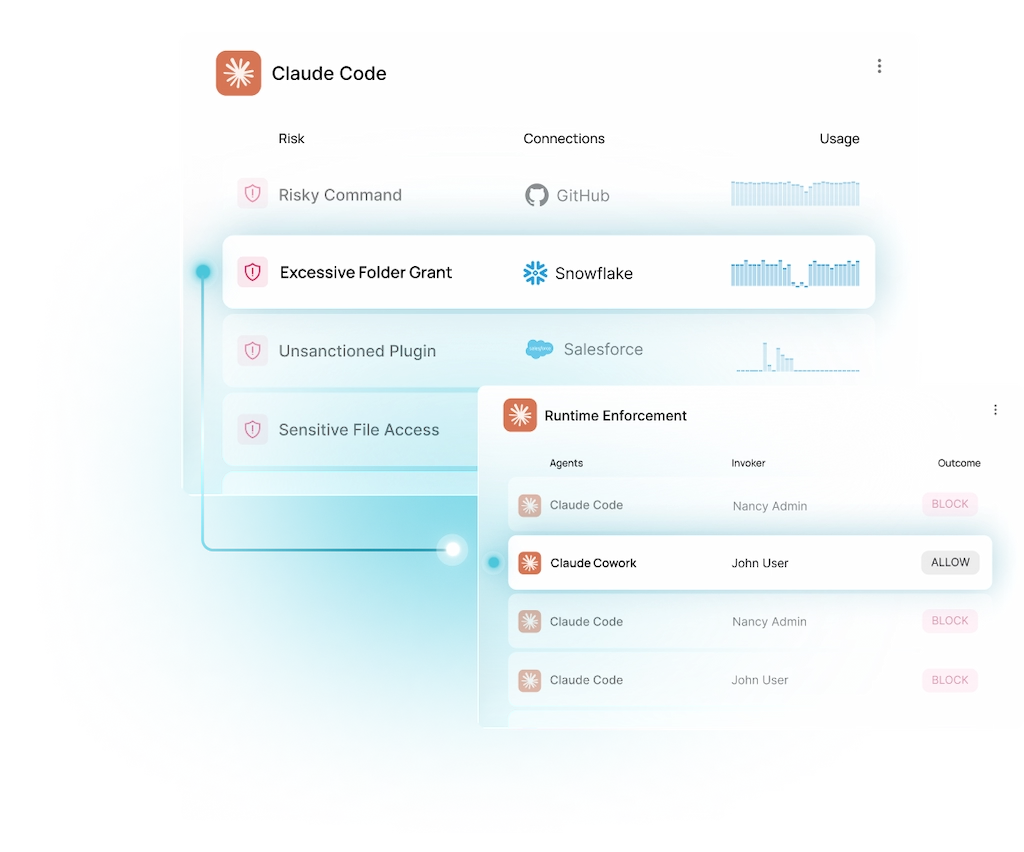
A mistaken or misled agent can do anything its user could in apps like Salesforce and Snowflake.
Claude agents without guardrails
With Obsidian
A report reviewed the next morning arrives after the data has left or the table is gone.
Developers connect Claude to company apps and MCP tools on their own, so those agents act without any security decision.
Claude Code can read SSH keys into its context, and Cowork can query a Snowflake table and post the results to Slack.
Each Claude tool call is checked against your policies before it runs.
Unsanctioned MCP servers and apps are found, and calls to them can be blocked.
Each agent’s access to credentials and sensitive data is mapped, so you can scope it down.
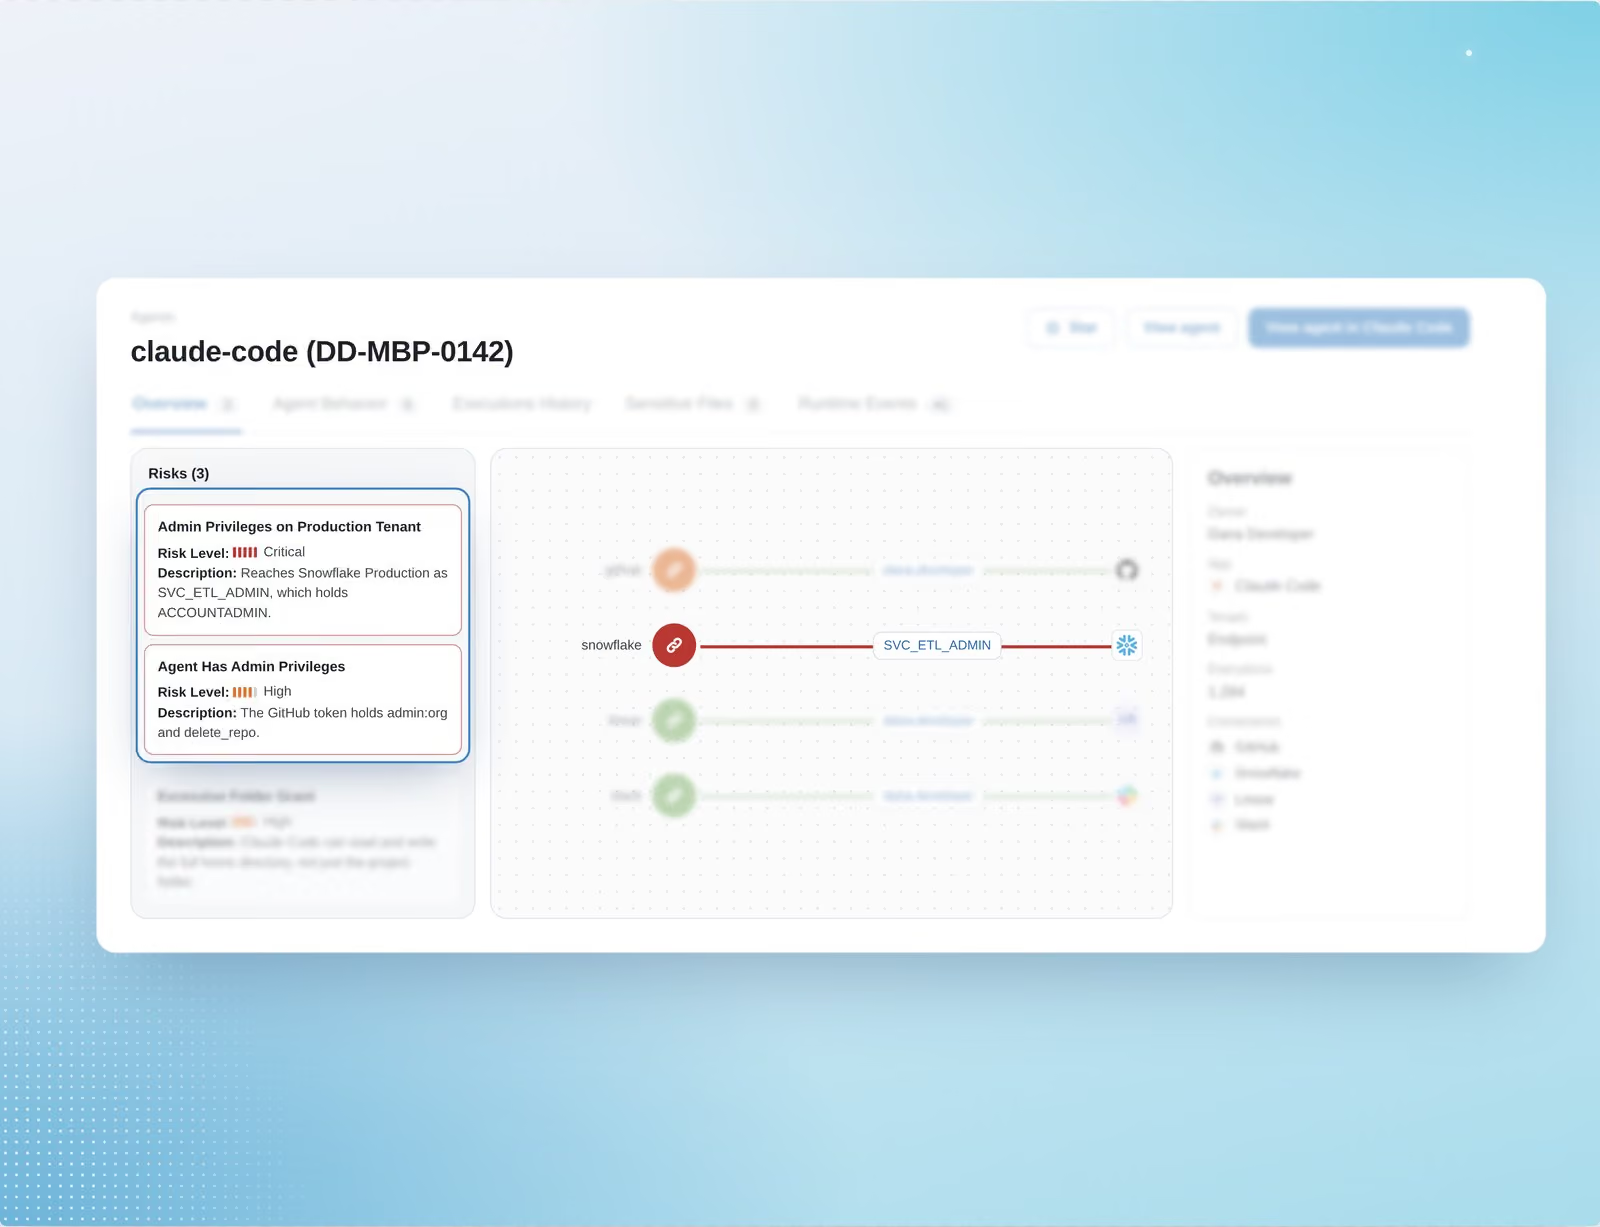
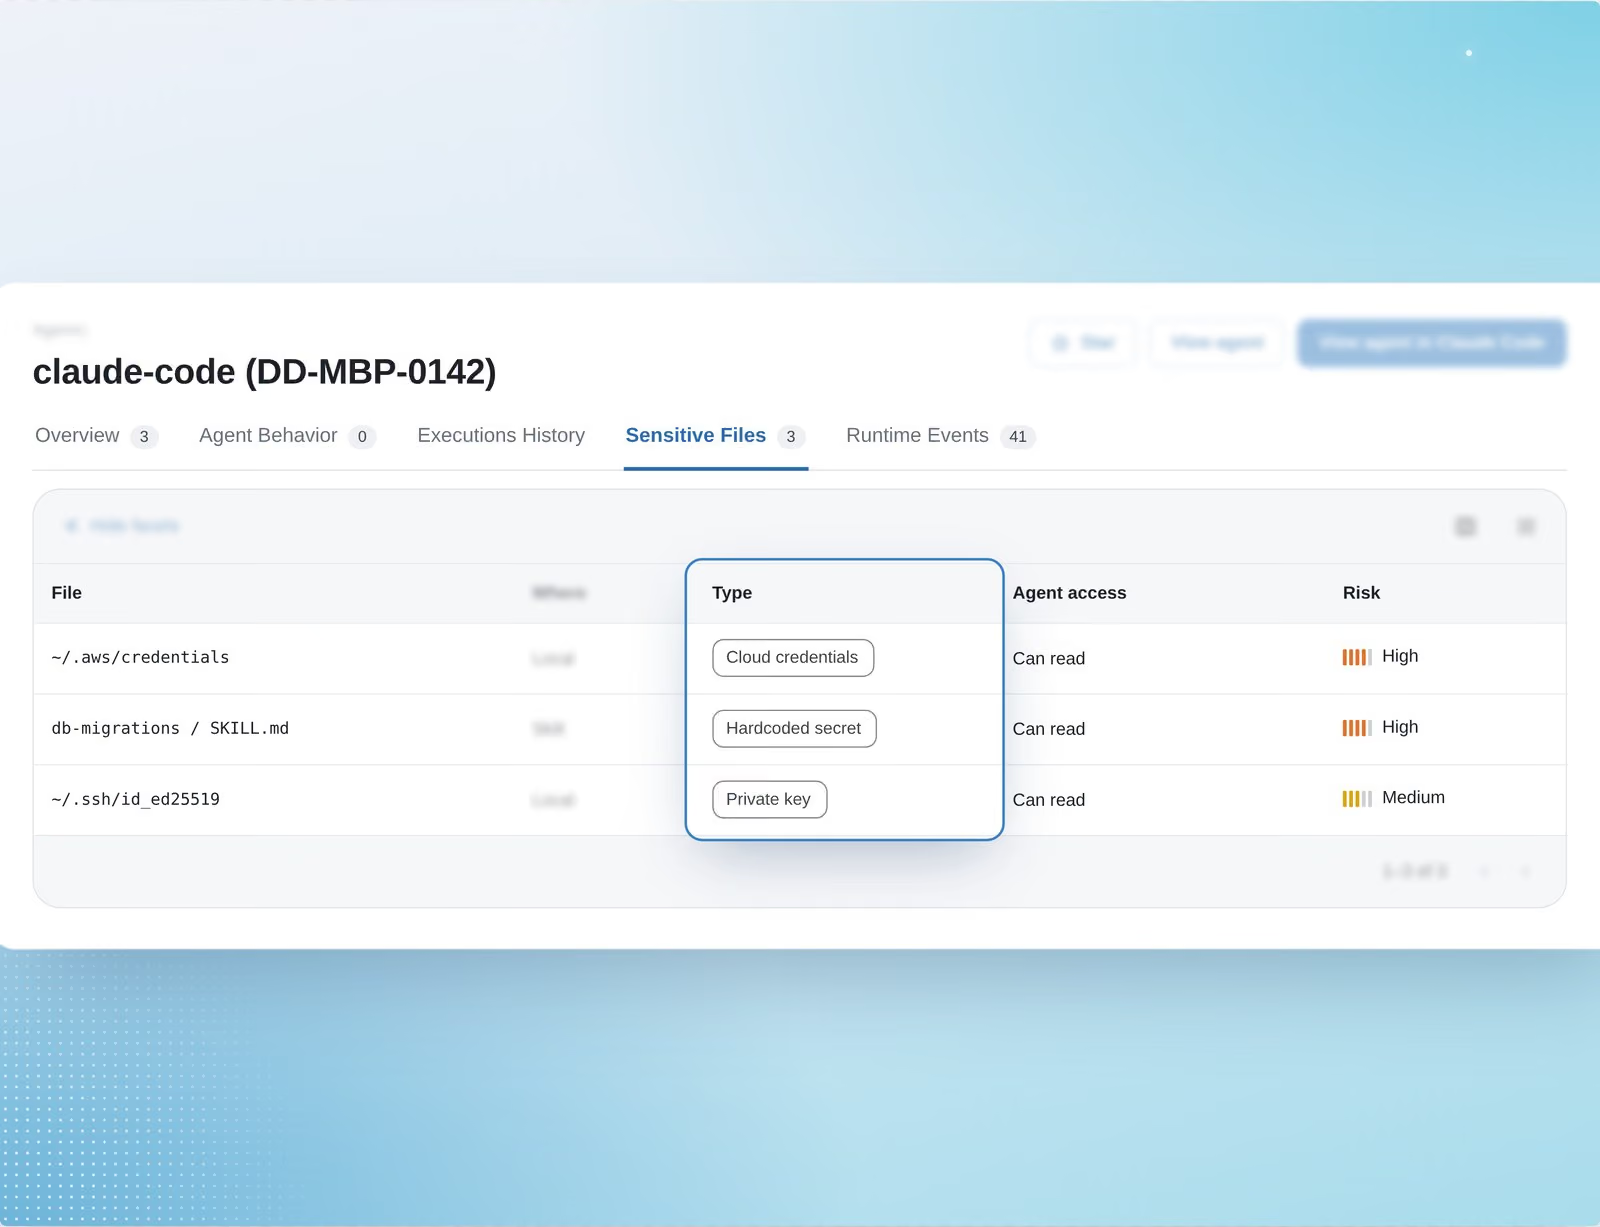
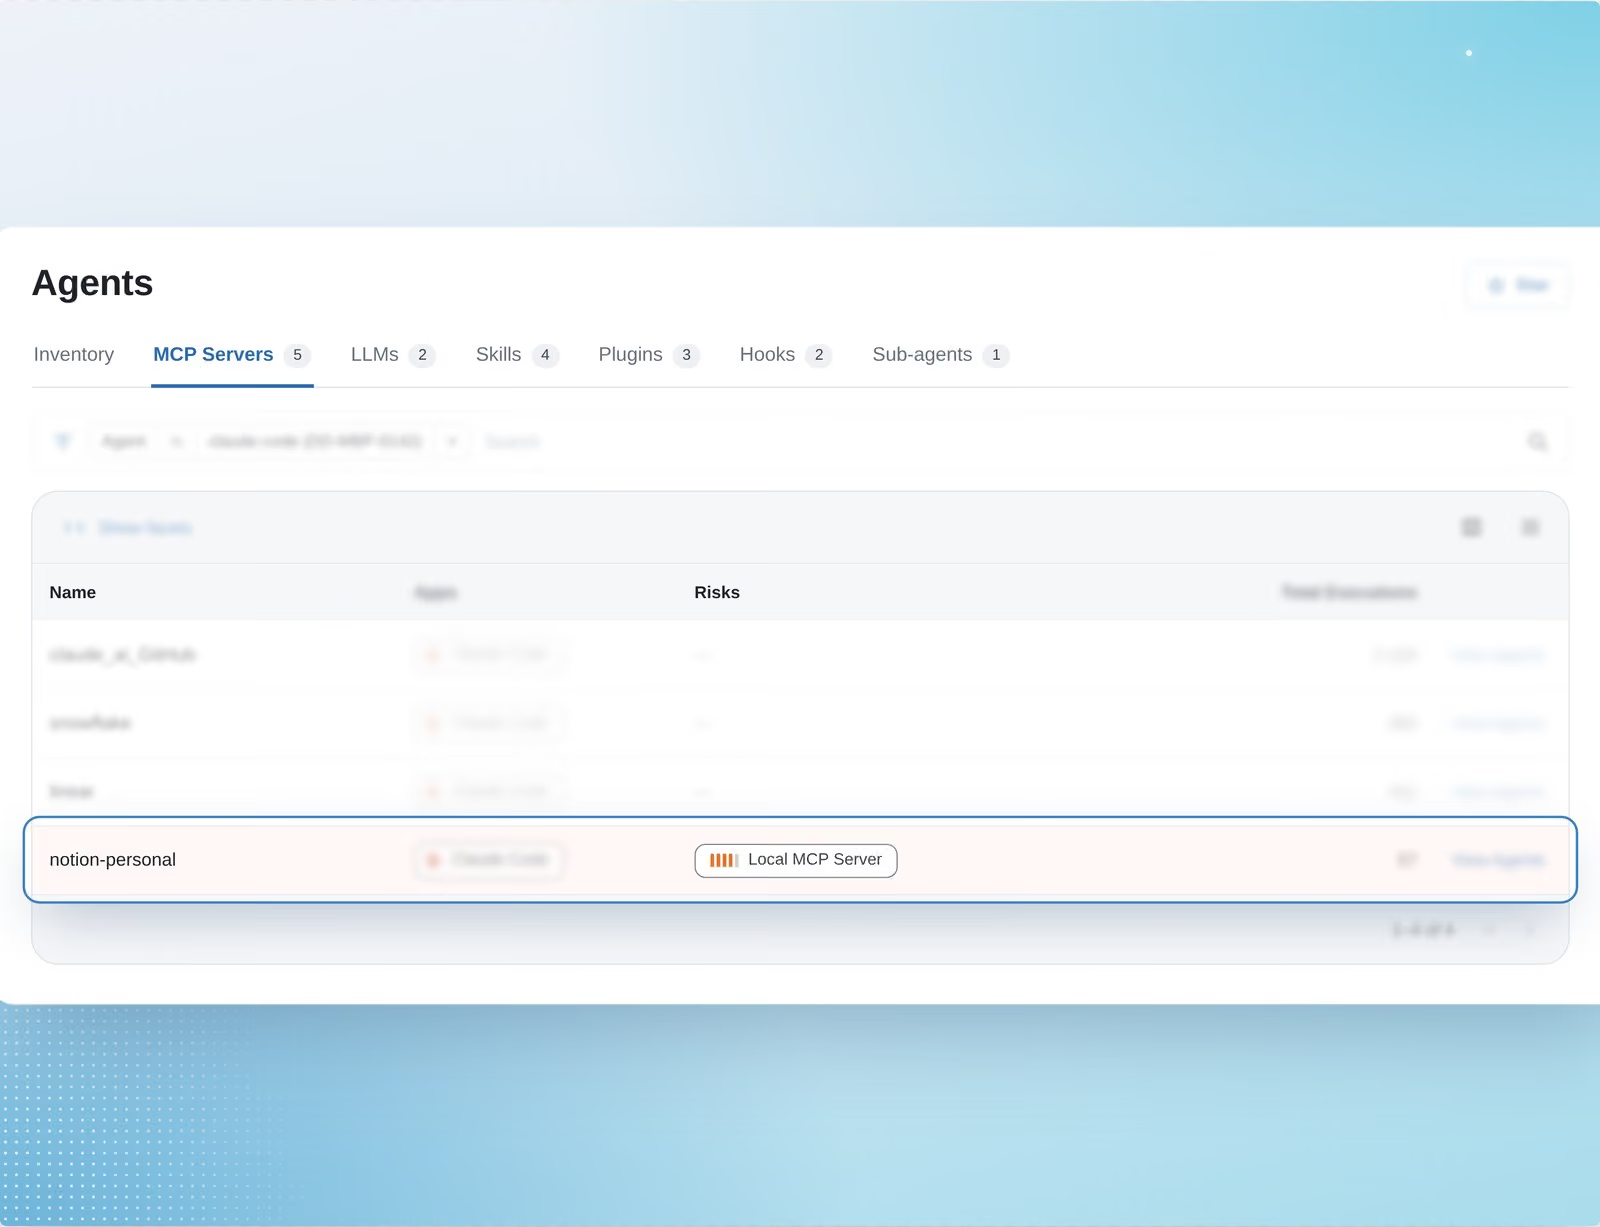
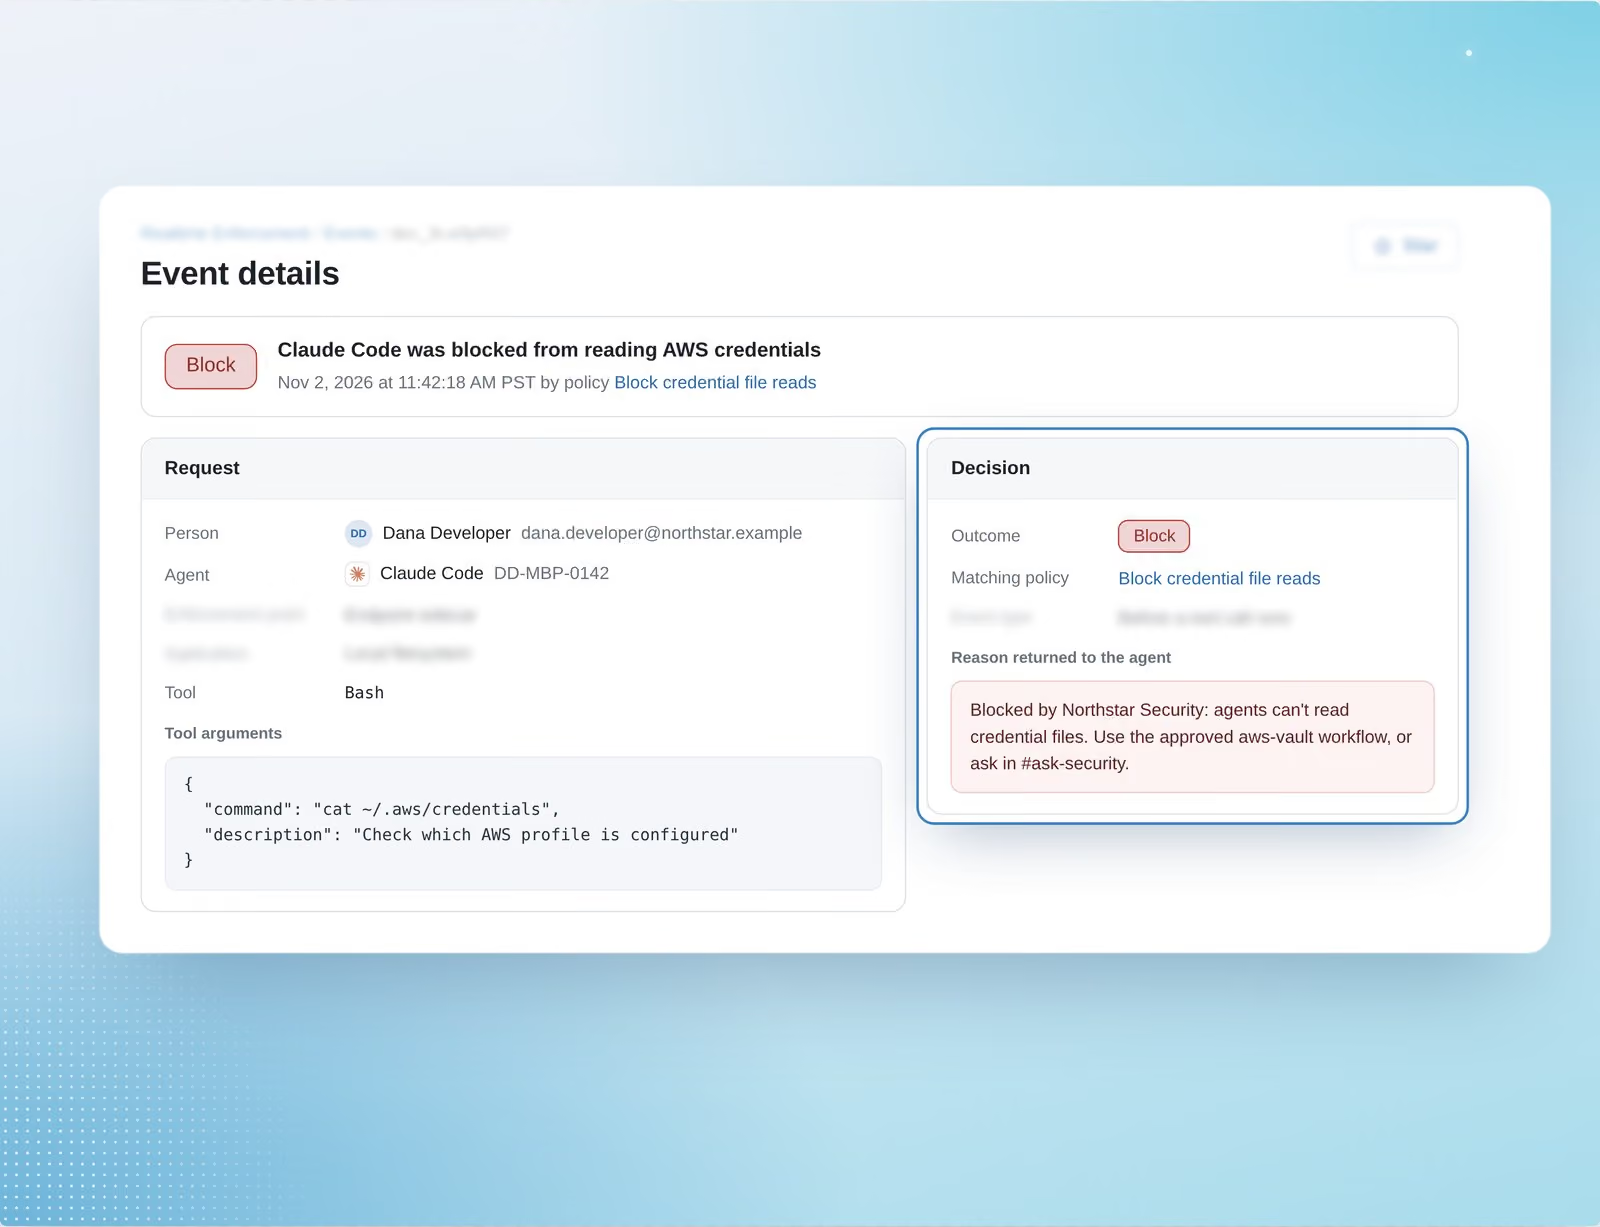
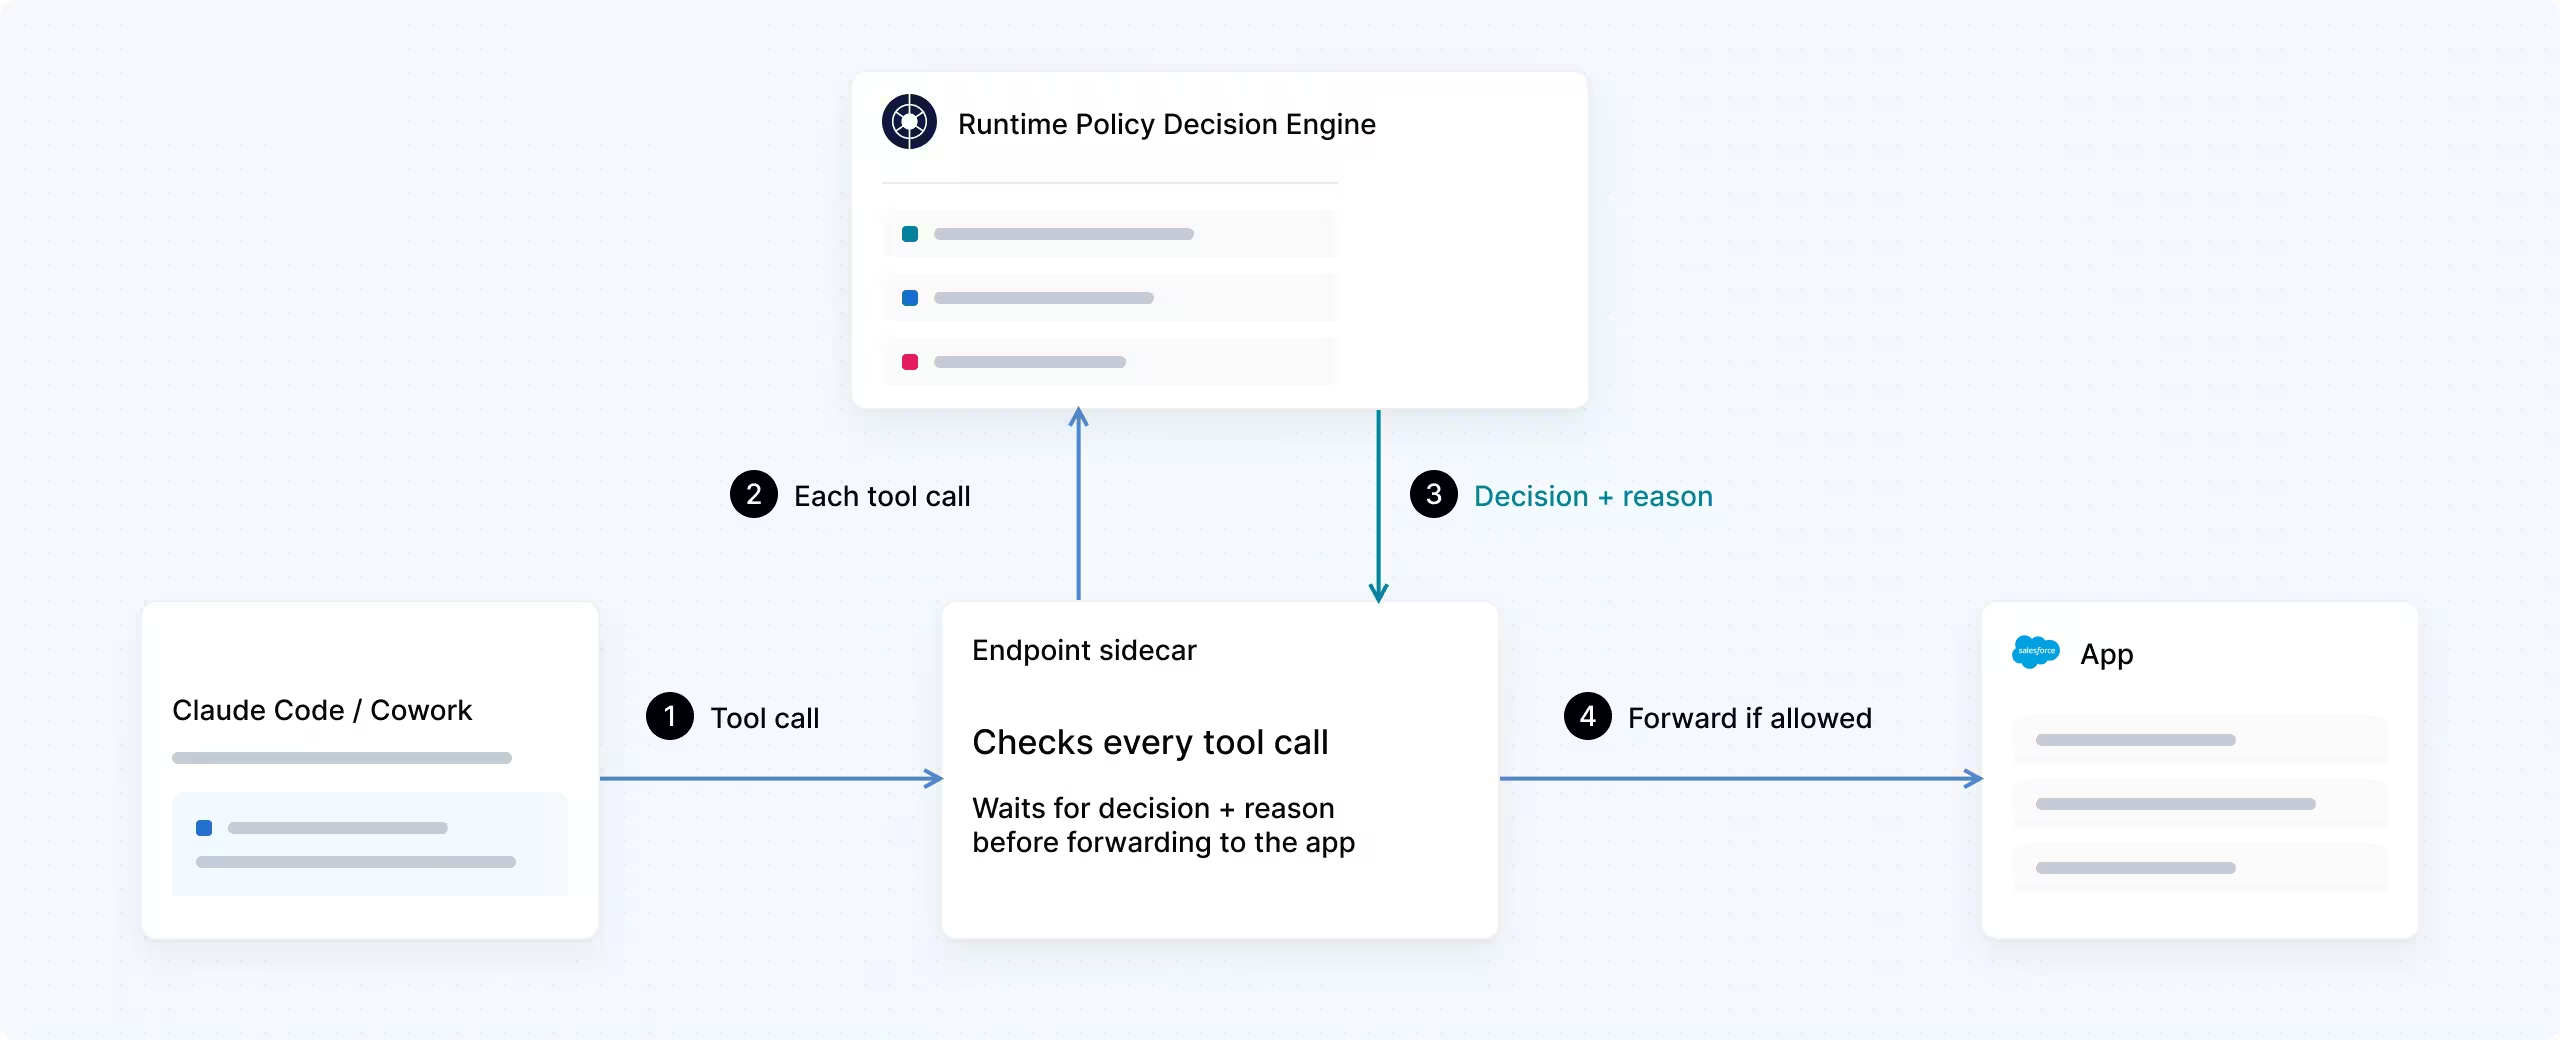
Claude agents act through MCP, OAuth, and direct integrations, and each of your controls sees only part of the action. Obsidian keeps those controls and adds one decision that sees the whole chain: person, agent, credential, tool, app, and data.

Both get agent discovery and governance, plus runtime enforcement through a sidecar that checks each tool call before it runs. Require approval is available for Claude Code policies that run before an operation. Cowork policies can flag or block.
Set the policy to Flag. It records matches on real Claude traffic without stopping anything, so you can confirm it catches the right actions before you switch it to block.
Available identity, HR, and application context, plus labels you supply, such as data classification. Which signals a policy can use depends on the integration.
No. Obsidian works alongside them. It narrows the access Claude agents hold across your apps and checks the actions that remain against your policies.
Obsidian inventories the MCP servers your Claude agents use and flags unsanctioned ones. For supported apps, the MCP Security Proxy identifies the user, keeps the app’s token out of the AI client, and checks each tool call against policy.
